Financial services handle some of the most sensitive data imaginable – bank accounts, investments, tax records, and personal financial information. Secure file sharing isn't optional; it's a regulatory and ethical requirement.
Regulatory Requirements
Common Regulations
- SOX (Sarbanes-Oxley) – Financial reporting controls
- PCI-DSS – Payment card data security
- GLBA – Customer financial privacy
- SEC regulations – Securities industry requirements
- State regulations – Various state-level requirements
Common Requirements Across Regulations
- Encryption for sensitive data
- Access controls and authentication
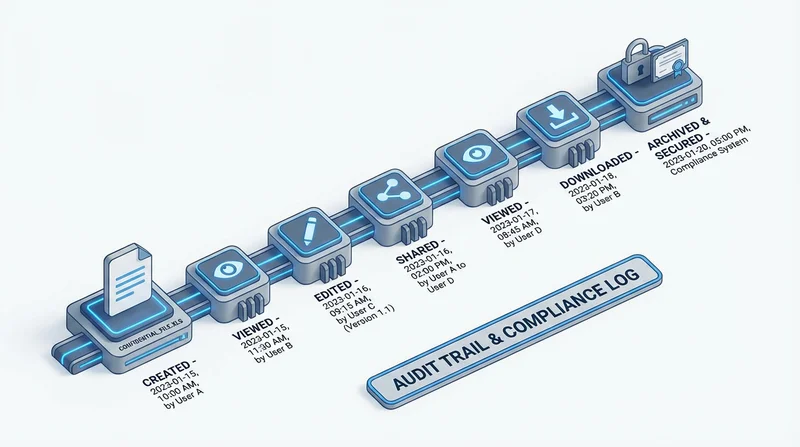
- Audit trails of data access
- Data retention policies
- Incident response procedures
Security Best Practices
1. Encryption is Mandatory
Use services with encryption in transit and at rest. GetShared provides TLS 1.3 for transit and AES-256 for storage.
2. Strong Authentication
- Require two-factor authentication for all users
- Strong password policies
- Regular credential rotation
3. Access Controls
- Password protect all external shares
- Set short expiration dates
- Implement role-based permissions
- Revoke access promptly when no longer needed
4. Audit Trails
Maintain complete records of:
- Who accessed what files
- When access occurred
- What actions were taken
See audit trail importance and use download tracking.
5. Data Classification
Classify financial data by sensitivity and apply appropriate controls:
- Public information – Basic protection
- Internal – Access controls
- Confidential – Encryption + access controls
- Highly sensitive – Maximum protection, limited access
Common Scenarios
Sharing with Clients
- Password protect all client documents
- Set expiration after expected review period
- Track downloads to confirm receipt
- Use branded pages for professionalism
Internal Collaboration
- Team folders with proper permissions
- Version control for documents
- Clear naming conventions
Regulatory Submissions
- Secure transfer methods
- Documentation of submission
- Audit trail maintenance
GetShared for Financial Services
- AES-256 encryption at rest
- TLS 1.3 in transit
- EU data centers for data residency
- Complete audit logging
- Access controls with passwords and expiration
- 2FA support
Employee Training
Train all staff on:
- Data handling requirements
- Security feature usage
- Incident reporting
See training guide.
Conclusion
Financial file sharing requires:
- Understanding regulatory requirements
- Implementing technical controls
- Maintaining audit trails
- Training employees
- Regular compliance reviews
See also: breach prevention, security best practices.